
RFC1 was published in April 7, 1969. We’ve come a long way since then :)
The story about Ping
Today I read “The story about Ping” to child[0] for the first time. It was well received! This comment explains why this tale is of interest to system administrators who are also fathers :)
2-2
Arsenal FC vs FC Barcelona χτες.
Έχω ένα φίλο που προσπαθεί να καταλάβει γιατί παρακολουθούμε ποδόσφαιρο. Για αγώνες σαν το χτεσινό που τους πετυχαίνουμε μια στα 10 χρόνια. Και που μια στα 20 (30, 40 , 50, …) ελπίζουμε να είναι η ομάδα μας μία από τις δύο.
Πίσω στη φτώχεια στο θέαμα της Super League τώρα…
The Cognitive Style of PowerPoint
Every student is required to read this (before being contaminated by PowerPoint).-
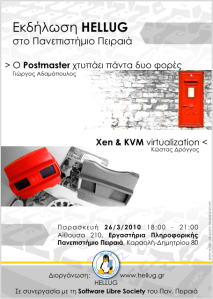
A Postmaster strikes twice
Mary Tsingou
Since today is Ada Lovelace Day, it may be worth reading about Mary Tsingou: “Fermi, Pasta, Ulam and a Mysterious Lady” [pdf]
Winning as a CISO
“Winning as a CISO” (Chief Information Security Officer) is the second book† I have bought from the ISACA bookstore. The book’s opening phrase is “If performing vulnerability assessments, configuring firewalls and performing network forensics makes you happy then becoming Chief Information Security Officer may not be the right career choice for you”. That may be true and has been stated in other fields‡ too, but it does not mean that this is not a book for security professionals not on the CISO career path.
In fact this is a book on understanding corporate management and not only for security people, but for other techies too! What this book tries to put into the reader’s mind is the simple fact that anything you do in a sufficiently large (or beaurocratic) organization is a service that you sell inside the organization. For your service to sell it does not only take hard work; Hard work is fine but can only get you so far. People who understand the organizational dynamics and politics are the ones who can both increase their budget and advance their careers. In his “Time Management for System Administrators” Tom Limoncelli mentions the martyr complex that many sysadmins seem to suffer from. Martyr complex is the result of both lack of automation of routine stuff that devours our time unproductively and the lack of effectively communicating of what it is exactly that we do*. Well guess what: It is not their job to try and understand what we do; it’s ours and in the security arena it is even harder because the “security guys” are the ones who block other people’s fun work for obscure reasons contained in dusty policy tomes.
“Are you the type of person that can stand up to superiors without being afraid of risking employment status? Will you stand up for an employee who acted with reason and responsibility but erred nonetheless?” This is a question that the author asks to anyone that considers a CISO career path. Well I have stood up to management (but not without personal loss) and my managers have stood up for me when I made errors. In fact one of them argues that “the only person that never errs, is the one that never does any actual work”. This is the kind of management that wins your team’s heart (any team, not just the security team).
Now I understand that the book belongs to a class that, as my friend XLA puts it, describe “an ideal corporation, in an ideal country where everyone eats ice-cream”, but nevertheless it is the thinking mode that matters. Do not let daily tactic stuff distract you from your target (strategy if you like). That and the realization that although hard work pays, it pays better when you invest in marketing it. I cannot say that I learned anything that I did not already knew from the book. But it is not always necessary for people to learn about such stuff from experience only.
[†] – The first one being Nigrini‘s book on Benford’s Law.
[‡] – “As long as technology is your thing, plan to die reading manuals”
[*] – “You do a lot of work, but not many people understand the work you do” from the opening of the speech from the Estonian Ministry of Communications representative at RIPE-54.
π

Russ Cox on regular expressions
Thanks to Ozan S. Yigit I found out about a three-article series by Russ Cox on regular expressions:
- Regular Expression Matching Can Be Simple And Fast (but is slow in Java, Perl, PHP, Python, Ruby, …)
- Regular Expression Matching: the Virtual Machine Approach
- Regular Expression Matching in the Wild
I knew about Russ Cox and his interest in regular expressions because of this link to a pdf copy of “Programming Techniques: Regular expression search algorithm” that I had found at his site. Somehow I had missed the articles. Using Ozan’s words “russ cox, like other top-notch cs people, takes a topic and nails it shut. these three papers are more valuable to me than any RE book”.
Yes the articles are that good. However the good news do not stop here. Russ Cox implemented a fast, safe, thread-friendly alternative to backtracking regular expression engines (like those used in PCRE, Perl, and Python) written in C++, called RE2. It even comes with a POSIX (egrep) mode.
The postmaster in me quickly thought of the possibility of implementing a milter that makes use of RE2, just like milter-regex uses traditional regex(3), but my time is so limited by other more pressing projects, that I can only wish that someone else undertakes such a task.
Universal Systems Language
While clearing my IEEE/Computer stack I read about the Universal Systems Language (December 2008 issue). Mind blowing stuff! USL and its Deal-Before-The-Fact methodology have their roots in the Apollo space program:
“We were the luckiest people in the world. There was no choice but to be pioneers. What would later become foundations for USL enabled the Apollo team to create the software for the trip to the moon.”
As is highlighted in the article “Correct use of USL eliminates the majority of errors, including all interface errors within a system modem and its derivatives”.
It is a pity that the 001 Tool Suite seems to cost $9950 :( That way we can only read (and dream) about it.

