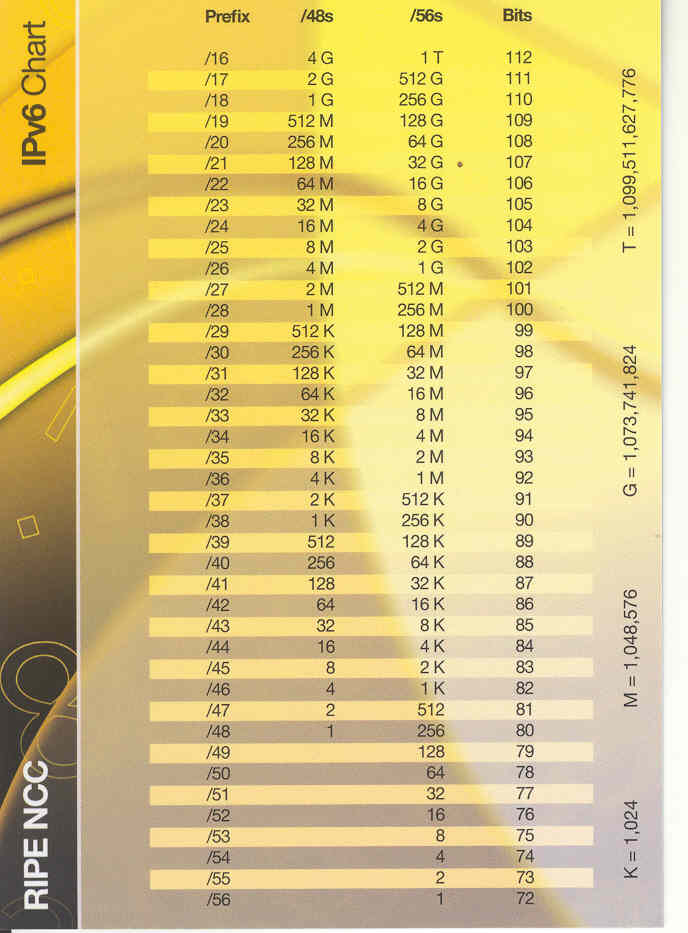
Also available: a printer friendly version. For an IPv4 version look here.

Fighting the automation paradox || Deployment θα κάνουμε φωνάζοντας "αέρα"
Also available: a printer friendly version. For an IPv4 version look here.
Another gem from Thursday’s and Friday’s training course: REX – the RIPE NCC Resource Explainer. Historical data on IP space allocated to you by RIPE NCC, reverse DNS stuff, inclusion to blacklists and other interesting data is there. Highly useful when you need to document certain decisions or recommendations to higher management since they come from an unbiased trusted third party. The kind of stuff you expect RIPE NCC to give back to its members.
Today’s RIPE training course included a very interesting exercise:
We will run out of available IPv4 addresses before we run out of the need for IPv4. But we may be able to make more efficient use of the IPv4 addresses we already hold.
Within your group, think of areas in your network where you could reclaim IPv4 addresses. This can be done by changing some parts of your network to use private IPv4 address space, or you could change the way you have subnetteed, or some other way entirely…
Also think of which networks can already be completely migrated to IPv6 (not dual stacked!) without any problems.
You and your group have 10 minutes to come up with all reclaimable IPv4 addresses in your networks.
For each area, we’d like to know:
Within these 10 minutes I was able to locate about 3 (maybe 4) /24 networks that could be reclaimed and I am sure that discussions with our routermasters will reveal some more. The time to act for IPv6 is now.

Best Current Practice: n.
The excuse we bring on the table when we do not want to explain our decision: “It is the best current practice!”
Κρίμα :(
Despite the toxicity that certain meetings carry, I’ve decided to try and make the most out of them. In a meeting that I attended the other day the question arose:
– What is an Incident?
So how does one define a security incident? The easy way out is “an incident is when I say it is”. Would you easily define as an incident every policy violation? Do automated ssh scans count as incidents? Or do we care for the interesting ones only?
How do you define an incident as such?
We knew for ~30 years that a day like yesterday would come. We just hoped that it would come later.
Mark Crispin writes:
“In particular, doing things with mailboxes in the hundreds of MB in that format takes a while. The authors of Outlook and Thunderbird are victims of a computer science course mindset which, starting in the 1980s, taught their pupils that all protocols are (or should be) stateless. Thus, they believe that IMAP is like HTTP; that when a server fails to respond immediately, that means that the correct remedial action is to disconnect and try again, or just disconnect and assume that everything happened anyway.”

