

Rule.-
nmap book
This landed today at nmap-hackers: Fyodor finished “Nmap network scanning” and it is shipping. From the book’s abstract:
Nmap Network Scanning is the official guide to the Nmap Security Scanner, a free and open source utility used by millions of people for network discovery, administration, and security auditing. From explaining port scanning basics for novices to detailing low-level packet crafting methods used by advanced hackers, this book by Nmap’s original author suits all levels of security and networking professionals. The reference guide documents every Nmap feature and option, while the remainder demonstrates how to apply them to quickly solve real-world tasks. Examples and diagrams show actual communication on the wire. Topics include subverting firewalls and intrusion detection systems, optimizing Nmap performance, and automating common networking tasks with the Nmap Scripting Engine.
16 – game over
Κάποιος κάποτε αποφάσισε πως ένας άνθρωπος είναι ικανός να φέρει όπλο για να επιτελέσει την εργασία του.
Τώρα ένα παιδί είναι νεκρό.
Αύριο θα είναι τα δικά μας παιδιά.
O Μπαμπάκης ρωτάει γιατί μένουμε εδώ ακόμα. Δε θα φύγουμε εμείς από την πόλη μας. Δε θα φύγουμε εμείς από τη χώρα μας. Αυτοί θα φύγουν.
Νύχτα.
Μια εκλογική εμπειρία…
– Τι επιτροπή είναι αυτή για την οποία ψηφίσαμε;
– Για την Υγιεινή και την Ασφάλεια της Εργασίας (Ν.1568/1985)
– Επιτροπές χωρίς λεφτά τι αξία έχουν;
Συγκρατήθηκα…
Για την ιστορία και προς μεγάλη μου έκπληξη, εκλέχτηκα σε αυτήν την επιτροπή (συγκροτήθηκε για πρώτη φορά από το 1985). Για να δούμε τι θα καταφέρουμε.
The New School of Information Security
I just finished reading “The New School of Information Security” which is written by Adam Shostack and Andrew Stewart. Reader of this blog thanasisk and I disagree on the value of the book. He considers it as overrated while I say that it is simply different.
I read this book in the bus (while going to work and returning from it). First of all, it is not a book. I would call it a long paper (160 pages long). Second, every two or three pages the message of the book repeats itself: We need objective data. If one wants to summarize “The New School” in two bullets, these would be:
- We need objective data, so let’s start sharing data and not wait for others to share first.
- Amateurs study Cryptography; Professionals study Economics.
Actually the second bullet is the title of chapter 6. People forget that cryptographers study cryptography. We apply it!
So does this book bring any new knowledge on the table? It depends on who you are. For me, who has passed from a variety of information security outposts (from security oriented system administration, to running an emergency response team and passing the CISA exam among others) the book does not offer any new knowledge. It clearly points out the “generalist versus specialist” debate (if you read sage-members sometimes such threads occur) and pushes the reader to think outside of his domain of expertise.
Information Security is always a lot more than what you deal with. So what did I get by reading the book?
- Although it discusses issues that “I know about” this is the first time that I see them written down, all of them and in a clear way. All the arguments that I previously needed in debates with non-security oriented people above me in the management scale are here. Now I have an arsenal of arguments that does not live in my brain.
- When you hear of “best practices” or “rules of thumb”, always ask for proof.
- It reminded me to try to avoid groupthink. Does one need a reminder for that? Well I think by the very definition of groupthink, yes.
- It exposed me to the principal-agent problem. It does explain a lot of the organizational behavior that I observe.
- It hints game-theoretic equlibria that explain the current no-win situation for everybody by the lack of objective data that will help us make any educated information security oriented decision.
- It provided pointers to four excellent papers:
So is this book overrated? Well if you have the experience that thanasisk carries you can live without reading it. Is it different? Since it is a 160 pages long paper (manifest if you like) of course. Is it readable? Yes! Should you read it? If you are an eager mind dealing with system administration or information security (at any level; from junior to senior) definately yes! It will always remind you that Information Security is a whole lot more than what you think it is, dealing or interested with. For it certainly is not only writing policies, running a vulnerablity scanner or finding that next buffer overflow that will give you root access.
For me the most powerful statement of the book remains the title of chapter 6:
Amateurs study Cryptography; Professionals study Economics.
PS: Adam Shostack blogs interesting stuff over at Emergent Chaos.
Ο στίβος ήτανε βαρύς
(…)
sendmail: when local users are not users of the system – part 2
Continuing from the previous post in this series, let’s see how one can deal with incoming email that must be delivered both to physical users of the system and users not visible via /etc/passwd:
LOCAL_CONFIG
Kuser user -m -a.FOUND

LOCAL_RULE_0
# Unconditionally redirect email to abuse and Postmaster
RPostmaster  < @ $=w . > $*        $: Postmaster  < @example.com. > $3
Rabuse  < @ $=w . > $*        $: abuse  < @example.com. > $3

# Deliver email to yiorgos locally
Ryiorgos  < @ $=w . > $*        $# local $: $1

# Delete email directed to all other users in /etc/passwd
R$-  < @ $=w . > $*        $(user $1 $)
R$- . FOUND        $#local $: bit-bucket

# The following is valid only if sendmail is instructed to not check /etc/passwd.
# This is achieved with MODIFY_MAILER_FLAGS(`LOCAL', `-w')dnl
R$- < @ $=w . > $*        $#custom.local $: $1
What does the above snippet do? The first set of rules accepts all incoming email addressed to Postmaster and abuse and redirects it to Postmaster@example.com and abuse@example.com.
The second set of rules accepts and delivers locally all incoming email addressed to user yiorgos.
The third set deletes all incoming email for all other users listed in /etc/passwd. One may refine that using a (sendmail) class definition and decide to do so for incoming email addressed to users like man, daemon, lp etc. Remember that in Ruleset 0 you cannot call $#discard.
Assuming that you have written a special delivery agent (to save email in a database for example) for “local” users not found in /etc/passwd, the last rule calls that delivery agent for the given username.
Of course if you are in a certain mood of BOFHiness, you can add similar rules that return random error codes to the sender. The expressiveness of sendmail’s modem-noise is unlimited…
(part 1)
sendmail: when local users are not users of the system
Suppose that you are running a sendmail server which is the final delivery server and that the users of the mail system are not physical users on the server (ie. they do not exist in /etc/passwd). What choices do you have in order to accept valid local email?
- Use LDAP.
- Edit mbdb.c and add a map. You can add your custom map and the relevant hooks to support the external directory of your choice. Read the source on how to do that.
- Edit mbdb.c and wrap getpwnam(3). Similar to the above but it may seem easier in some cases, especially if the users are kept in /etc/passwd like file. The first time I saw such a trick was when I was reading TACACS+ code.
- Use MAILER(`local’) without the w flag, which means that /etc/passwd is not consulted prior to forking the mail delivery agent. This is accomplished by:
MODIFY_MAILER_FLAGS(`LOCAL’, `-w’)dnl
That way the local mailer and not sendmail decides whether the user exists or not. You have to write your own delivery agent.
Of the above choices I rely heavily on #3 (although I am not using flat files) and lately I used #4. LDAP is always my last choice. I am sure there are other choices though.
(part 2)
5-1
re: blogdeath
Διαβάζοντας το “Ενάντια στη μελαγχολία” του Ματθαίου Τσιμιτάκη, έπεσα πάνω στο σχόλιο του Μανώλη Ανδριωτάκη:
Γεννιέται ένα ερώτημα: Θα έπρεπε να περιμένουμε ποιοτικές διαφοροποιήσεις;
Από ότι καταλαβαίνω* ο Μ. Ανδριωτάκης τις περίμενε. Εγώ πάλι όχι. Ας δούμε γιατί:
Για την ανάλυση της άποψής μου θα χρησιμοποιήσω τον νόμο του Metcalfe ο οποίος μας λέει πως η αξία ενός δικτύου είναι ανάλογη του τετραγώνου (~n2) των χρηστών του συστήματος.
Εφαρμόζοντας το νόμο σήμερα θα μπορούσε να καταλάβει κανείς πως αλλάζει αξία το οικιακό του δίκτυο (π.χ. με τρεις υπολογιστές) συνδεόμενο με το Internet. Εάν για λόγους απλότητας πούμε πως η αξία του δικτύου είναι V(n) = n2, τότε από το 9, λόγω της συμμετοχής σε ένα ευρύτερο δίκτυο η αξία γίνεται πολύ μεγαλύτερη. Ανάποδα εάν το δούμε, το κέρδος για ένα μεγάλο δίκτυο δεν είναι ιδιαίτερα μεγάλο με την προσθήκη ενός κόμβου. Π.χ. η διαφορά (109 + 1)2 – (109)2 ~ 2 x 10⁹ αλλά η μεταβολή στην αξία του μεγάλου δικτύου είναι ελάχιστη (~ 2 x 10⁻⁹).
Αντίστοιχους υπολογισμούς μπορούμε να κάνουμε και για την μπλογκόσφαιρα (όπου μπλογκόσφαιρα ορίζουμε το σύνολο μπλογκς με μια κοινή ιδιότητα, π.χ. Ελληνική Μπλογκόσφαιρα). Γραφικά το κέρδος† (ποιότητα) για κάθε blog που προστίθεται σε ένα ήδη υπάρχοντα πληθυσμό από blogs, μπορεί να παρασταθεί ως εξής: 
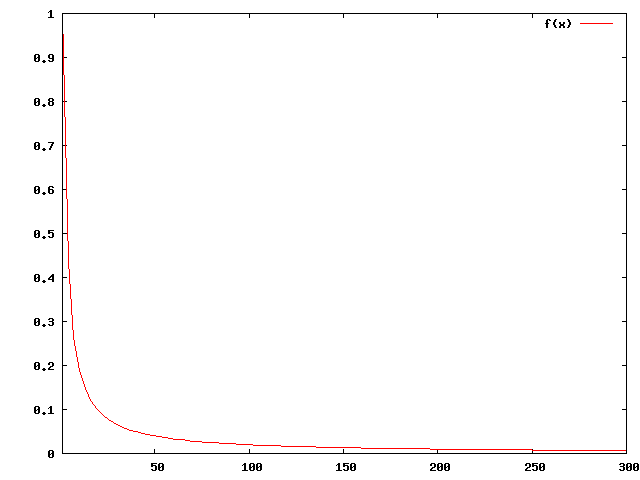
(Το 300 το διάλεξα γιατί κάπου εκεί, αλλά λιγότερα, είναι τα feed που παρακολουθώ.)
Είτε έχουμε να κάνουμε με ένα aggregator που προσπαθεί να απεικονίσει μια μπλογκόσφαιρα, είτε έχουμε να κάνουμε με ένα προσωπικό feed reader, κάθε νέο προστιθέμενο blog προσφέρει ακόμα λιγότερο κέρδος από το προηγούμενο για το χρήστη. Και αυτός είναι και ο λόγος που τελικά αφαιρούμε feeds από τους feed readers μας. Γιατί μας ενδιαφέρει το fat head και όχι το long tail στις λίστες που φτιάχνουμε.
Εν τέλει, αυτό που θέλω να πω είναι πως το γεγονός πως οι ποιοτικές διαφοροποιήσεις (για οποιοδήποτε ορισμό της ποιότητας) δεν ακολουθούν τον ρυθμό αύξησης των ιστολογίων είναι κάτι αναμενόμενο που δεν πρέπει ούτε να μας εκπλήσσει, ούτε να μας απογοητεύει.
Related post: Metcalfe’s Law.
[*] – Ο Μ. Ανδριωτάκης λέει πως κατάλαβα λάθος.
[†] – Για τις ανάγκες αυτού του post οι έννοιες κέρδος και ποιοτική διαφοροποίηση ταυτίζονται.
[‡] – Ευχαριστώ Stazybo Horn για τη διόρθωση.

